Open-source tools for AI provenance, drift and secrets.
Three tools from ZettaCore Labs, each answering a question a delivery pipeline usually cannot: who signed off on an AI-assisted change, whether an LLM feature still behaves the way it did at the last release, and which code can read your secrets. All three are free, licensed for commercial use, and published with their limitations in writing.
The tools
Why we publish them
Each one started as a control we wanted while building AI, fintech and blockchain systems: a record of who reviewed AI-assisted code, a regression gate for prompt and model changes, and a way to keep API keys out of logs and child processes. Publishing them lets anyone see exactly how we approach these problems, and check the work, before an engagement starts.
How they are built
The same standard we hold client systems to. Each tool fails closed rather than passing on a bad input, runs in your own repository, CI or process with no hosted service behind it, ships versioned releases on PyPI or npm, and states in its documentation what it does not do.
What all three share.
Fail closed
An invalid signature, an unsupported provider or a missing variable stops the run. None of the three passes quietly when it cannot decide.
No hosted service
Everything runs where your code already runs. There is no dashboard to trust, no account to create and no telemetry.
Versioned, pinned releases
Released on PyPI and npm with changelogs. Attest and AIDrift publish immutable GitHub Action tags you can pin by commit.
Limits in writing
Each project documents what it does not cover, so a team can decide where it fits before relying on it.
Which tool answers which question.
| Tool | Answers | Language | Licence | Status | Install |
|---|---|---|---|---|---|
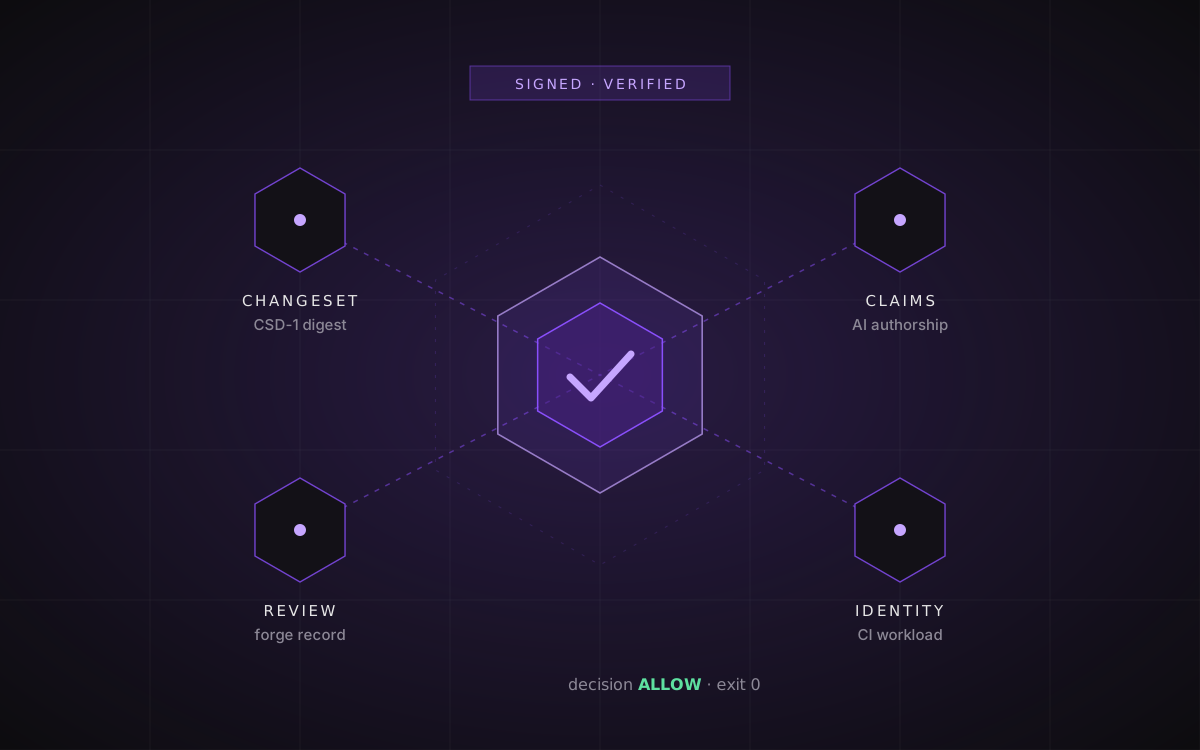
| Attest | Signs AI-authorship claims and human review evidence for every pull request with Sigstore, then gates the merge. | Python | Apache-2.0 | Pre-alpha, v0.1.7 | uvx --from attest-cli==0.1.5 attest init |
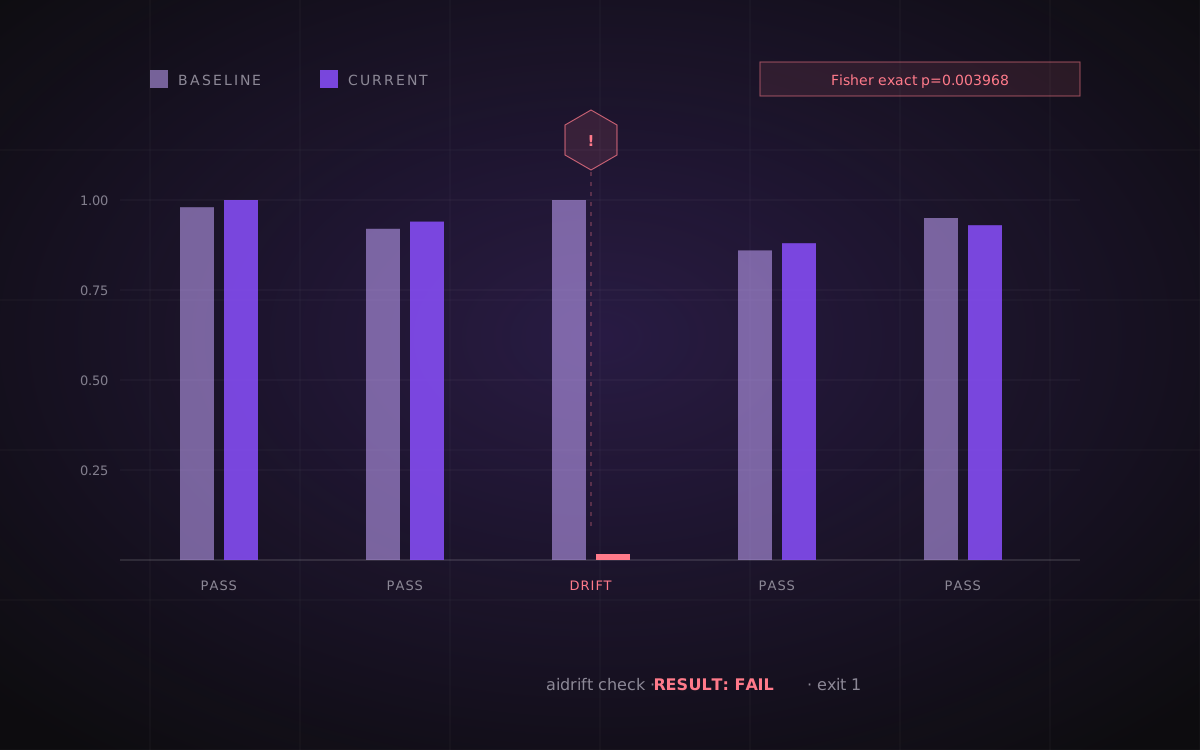
| AIDrift | Versions prompts and model settings, detects LLM behavior drift with statistics, and blocks regressions in CI. | TypeScript | Apache-2.0 | Public beta, v0.9.0-beta.1 | npm install --global @zettacore/aidrift@next |
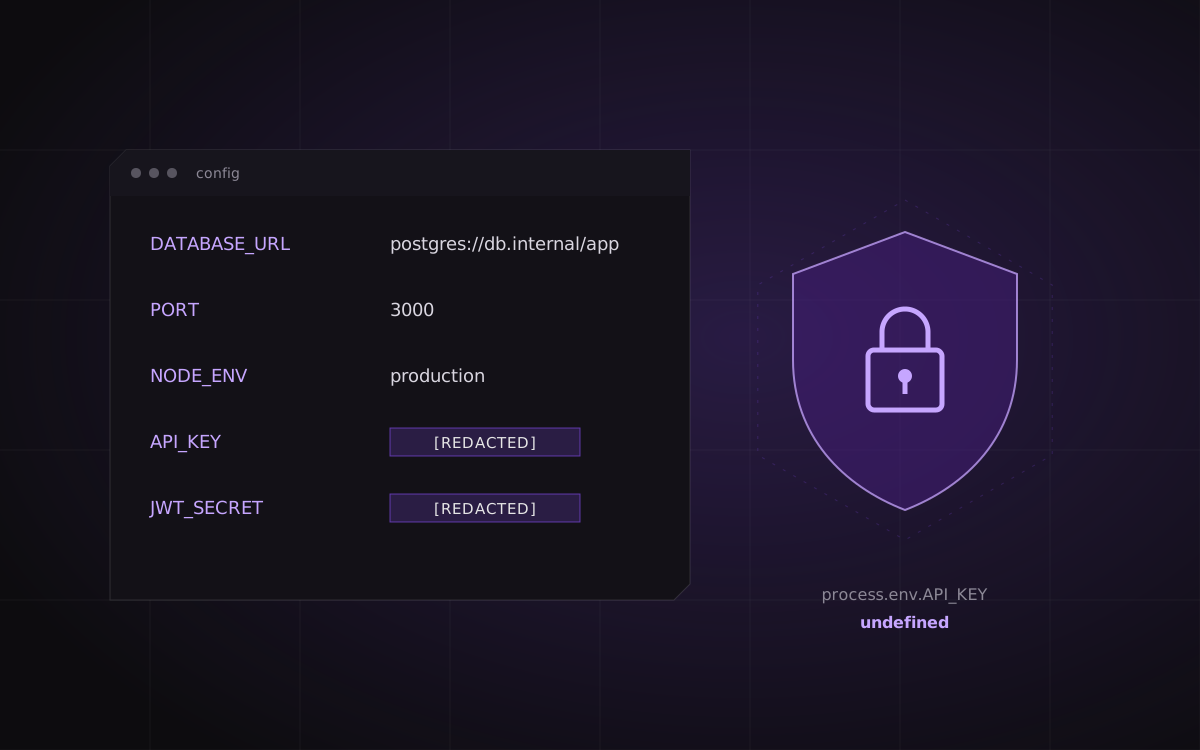
| ENVShield | A type-safe dotenv replacement: schema-validated config, secrets redacted everywhere, and removed from process.env. | TypeScript | MIT | Released, v0.1.1 | npm install @thekaloliya/envshield zod |
Questions we get asked.
Yes. Attest and AIDrift are licensed under Apache-2.0 and ENVShield under MIT. Both licences allow commercial use, modification and redistribution, provided the licence and copyright notices are kept.
Parth Kaloliya, founder and director of ZettaCore Labs, maintains all three on GitHub. Issues and pull requests are open on each repository, and security reports go through the private channel described in each SECURITY.md.
Not equally. ENVShield 0.1.1 is a small, dependency-free library on npm. AIDrift is a public beta (0.9.0-beta.1) and Attest is pre-alpha (0.1.7); both say which interfaces may still change. Each tool page lists its current status and limits.
Yes. All three are free to adopt on your own. If you want them wired into an existing CI pipeline, adapted to your review policy or extended for your stack, that is engineering work we take on as a normal client engagement.
Want these controls in your delivery pipeline?
We implement provenance gates, LLM regression testing and secrets hygiene for teams shipping AI and fintech systems. Tell us what you run today.